
AI is making vulnerability discovery extraordinarily fast. But finding vulnerabilities faster doesn’t mean we’re fixing them faster.
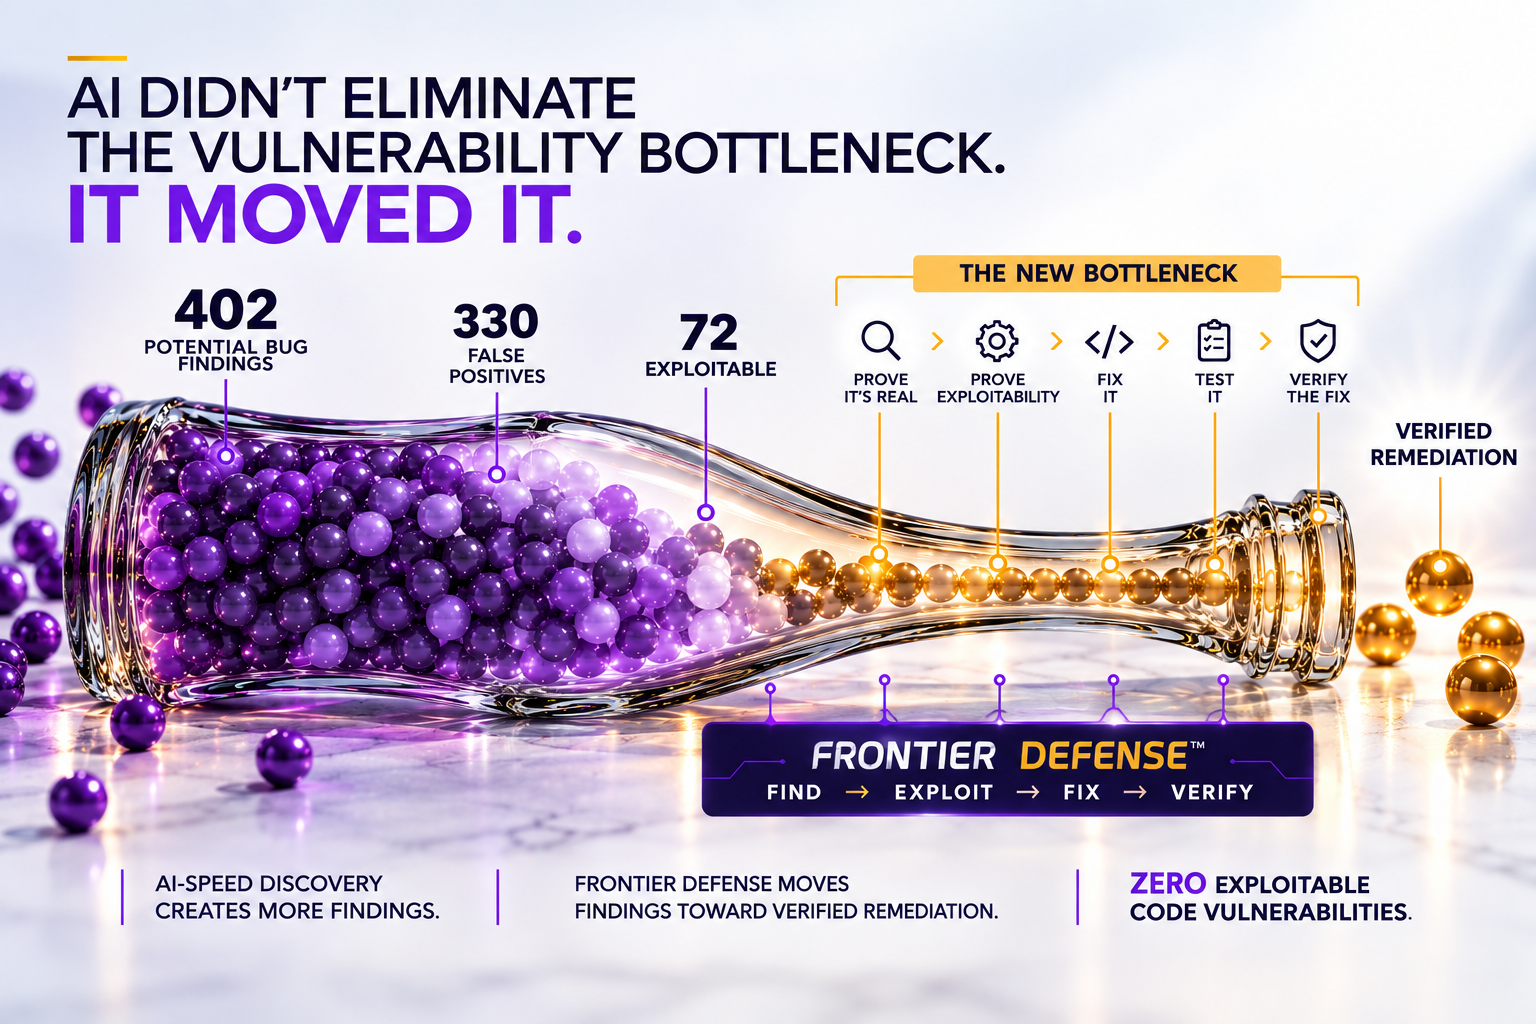
In Lineaje’s Frontier Defense evaluation across real-world open-source repositories, AI agents generated 402 potential exploitable findings. But generating findings was only the beginning.
The harder work comes next: determining whether a finding is real, proving exploitability, creating the right fix, testing it, and verifying that the remediation closes the vulnerability.
Discovery is getting faster. The bottleneck is moving downstream.
The Frontier Defense evaluation illustrates the scale of the challenge:
The distinction matters.
Finding a potential vulnerability is not the same as eliminating an exploitable one.
As AI increases the speed and volume of discovery, security and development teams can face a new challenge: processing findings fast enough to determine what is real, what is exploitable, and what actually needs to be fixed.
For years, application security has focused heavily on detection:
Find more. Find earlier. Find faster.
AI is rapidly changing that equation. AI agents can analyze code and surface potential vulnerabilities at machine speed.
But every finding can still trigger an operational chain:
FIND → PROVE → EXPLOIT → FIX → TEST → VERIFY
If the work after discovery remains slow or manual, faster detection can simply create a faster-growing queue of findings.
The constraint shifts from:
“Can we find it?”
to:
“Can we prove it’s real, prove it’s exploitable, fix it, and verify the fix?”
This is where Frontier Defense changes the workflow.
Rather than stopping at detection, Frontier Defense is designed to move through the remediation lifecycle:
FIND → EXPLOIT → FIX → VERIFY
It investigates whether a finding is real and exploitable, generates remediation, tests the resulting patch, and verifies that the vulnerability has actually been closed.
The goal isn’t simply more findings.
It’s verified remediation.
Security teams ultimately don’t need more vulnerability alerts. They need fewer exploitable vulnerabilities.
That changes what organizations should expect from AI-powered security.
Speed of discovery matters—but so does the ability to convert a finding into a validated, tested, verified fix without creating another backlog for developers.
AI-speed discovery needs an equally fast path to verified remediation.
Otherwise, organizations risk replacing the traditional vulnerability backlog with an AI-generated findings backlog.
AI didn’t eliminate the vulnerability bottleneck. It moved downstream.
As discovery gets faster, the differentiator becomes what happens after the finding:
FIND → EXPLOIT → FIX → VERIFY
Because a vulnerability isn’t eliminated when it’s found.
It’s eliminated when the fix is verified.
